Your quarterly close is underway. A partner is explaining a figure over video while colleagues upload large workpapers, and the screen freezes mid-sentence. The cloud application is available, the office internet connection is technically working, yet everyone experiences delay because every request is traveling toward the same distant services.
Network edge services address that problem by placing routing, processing, storage, and security capabilities closer to the people and devices using them. The result isn't automatically a faster network for every business, but it can provide more predictable performance when distance, congestion, distributed locations, or real-time applications create friction.
What Network Edge Services Mean in Plain Language
A centralized cloud works like one enormous warehouse. Your office sends every request to that warehouse, the warehouse processes it, and the response travels back. That model is efficient for many workloads, but the physical distance and shared network path can become noticeable during video calls, cloud transactions, remote desktop sessions, or device control.
An edge service moves part of that work closer to you. Instead of sending every byte to a far-away data center, the network can route traffic through a nearby location, apply security rules locally, cache frequently requested content, or run application logic near the customer. Distance equals delay, so shortening the journey can improve responsiveness before the application does any additional work.
Practical rule: Edge isn't about moving everything out of the cloud. It's about deciding which work benefits from being closer to the user, device, or branch.
The difference is easier to see in a business example. A regional accounting firm might keep its main records in a central cloud platform while using nearby network facilities to handle traffic steering, secure access, and selected processing tasks. Video traffic can take a more suitable path, while sensitive requests still follow the firm's security policy.
The term grew out of content delivery and edge-server architectures in the late 1990s. Straits Research's edge computing market overview notes that the first commercial edge computing services appeared in the early 2000s, supporting applications such as dealer locators, shopping carts, real-time data aggregators, and ad insertion engines. That history shows the shift from merely caching content near users to running application logic closer to customers.
The business question isn't whether every company needs a complex distributed architecture. It is whether a centralized design is creating a measurable problem that proximity, local control, or distributed security can solve.
The Core Building Blocks of an Edge Network
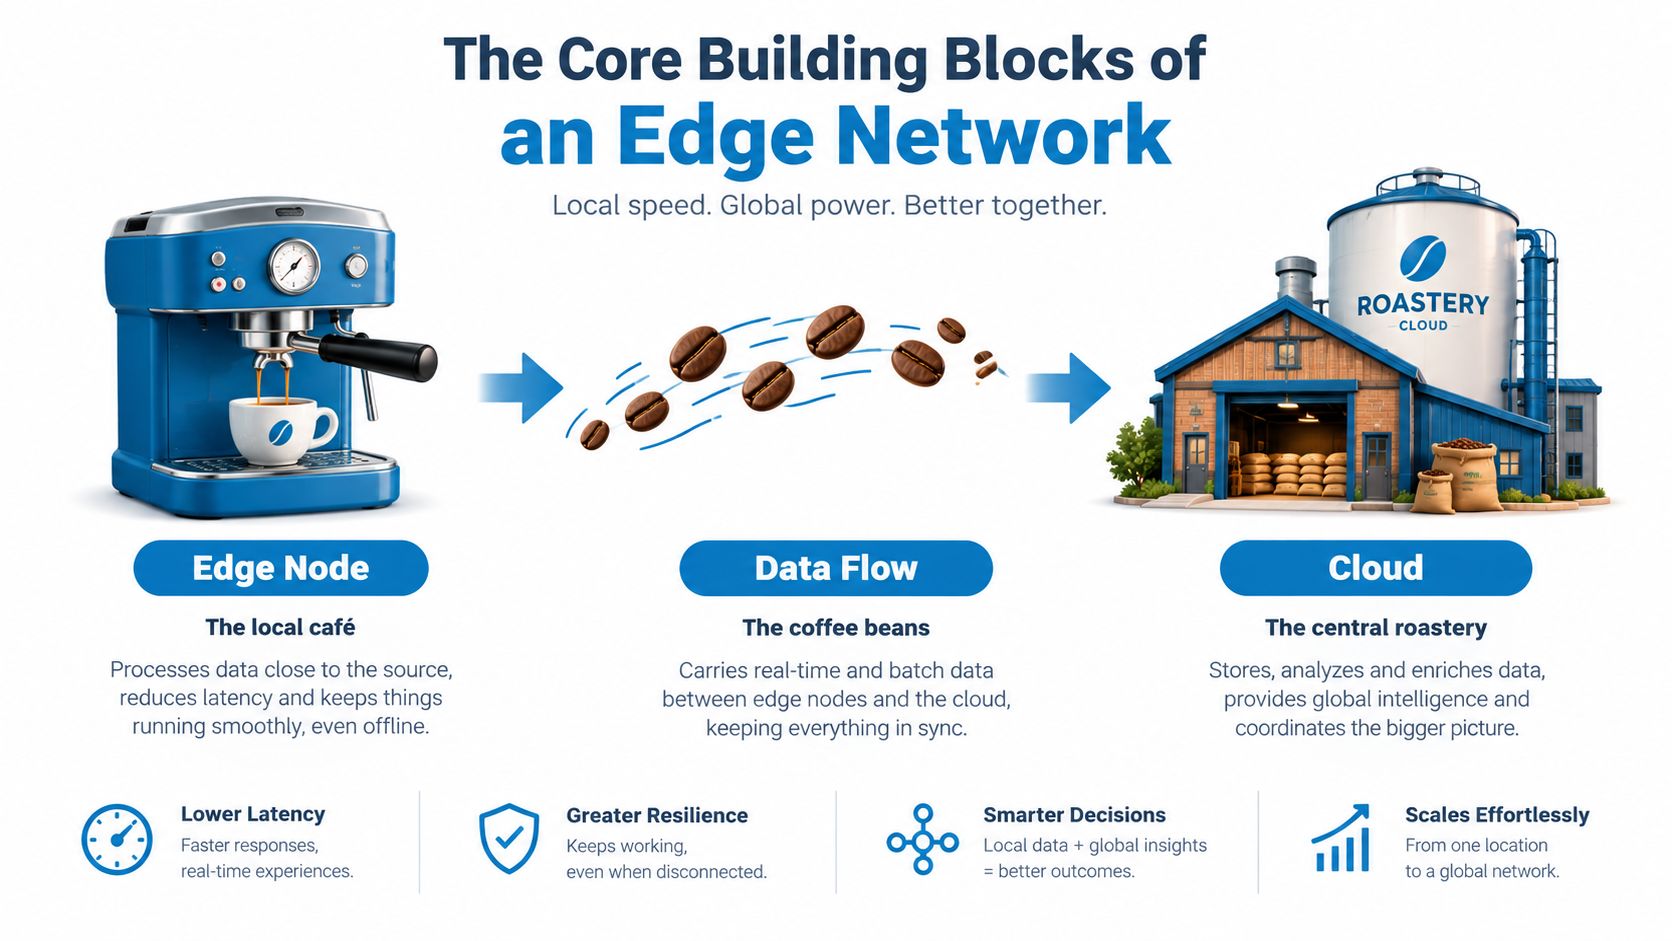
A coffee shop makes the architecture easier to understand. The central roastery is the cloud, where large-scale storage and processing happen. The espresso machine at the counter represents the edge, because it prepares an order close to the customer instead of sending every request back to the roastery.
Start with the nearby counters
A Point of Presence, often called a PoP, is like a local counter where customers connect to the coffee chain. Technically, it is a provider location where network connections, routing equipment, security functions, and sometimes compute resources meet. A provider may operate PoPs in different regions so users don't all have to reach one central location.
An edge server is the espresso machine. It runs software, handles requests, stores selected data, or applies application rules close to the user. A retailer might use one to deliver frequently requested storefront content, while an industrial operator could use local processing for sensor data.
Let the order queue do its job
Traffic steering is the queue manager. It chooses an appropriate path based on location, availability, application policy, congestion, or security requirements. If one route is busy, the system can direct traffic through another suitable path instead of treating every request identically.
Compute and storage are the grinder, milk, and refrigerator. Compute performs the work, while storage keeps data or cached content nearby. The local resources don't replace the central roastery. They handle the items that need quick preparation or frequent access.
Put security at the counter
Security enforcement includes firewalls, access controls, inspection, segmentation, and traffic filtering. In the analogy, locks and cameras protect the shop and separate staff-only areas from customer space. At the edge, these controls can inspect traffic near its entry point and limit how far a compromised device can move.
A business planning a wider rollout should also check whether its local connectivity can support the design. Practical guidance on how to upgrade business Wi‑Fi infrastructure can help teams improve the wireless layer that connects employees and devices to the edge. Even a well-designed edge service can't compensate for weak coverage or overloaded access points inside the building. Small physical components, including a micro USB cord for compatible equipment, may also matter during installation, but they aren't substitutes for sound network planning.
Together, PoPs, servers, traffic steering, capacity, and security form one operational fabric. The cloud remains the central roastery, while the edge prepares, protects, and routes the requests that benefit from a shorter trip.
How On-Prem, Cloud Edge, SD-WAN, and PoPs Differ
Buyers often encounter four architectures under the broad edge label. They overlap, but they solve different problems.
On-premises edge places hardware inside your building. A hospital running medical imaging workloads might process selected images locally because clinicians need fast access and the data may be too large or sensitive to send elsewhere first. The organization gets strong control, but it also owns equipment, maintenance, capacity planning, and failures.
Cloud edge services put provider-operated infrastructure near users. A retailer serving customers across multiple regions might use nearby cloud edge locations to improve storefront responsiveness and apply security policies without building facilities in every market. The provider manages much of the underlying platform, while the buyer pays for the service and configures its workloads.
SD-WAN, or software-defined wide area networking, manages traffic across multiple connections. A law firm with three offices and remote employees might use it to choose paths for voice, legal applications, and ordinary web traffic. SD-WAN is primarily a traffic management and connectivity approach. It can be part of an edge service, but it isn't identical to edge compute.
Carrier PoPs are shared gateways operated by a network provider. A startup that needs better routing into Microsoft Azure or Amazon Web Services might use a carrier PoP without deploying local application servers. This can improve network entry and exit points while keeping application processing centralized.
| Architecture | Control | Upfront Investment | Typical Latency Impact | Operational Complexity | Best Fit |
|---|---|---|---|---|---|
| On-premises edge | Highest | Higher hardware commitment | Strong for local workloads | High | Sites needing local processing and direct control |
| Cloud edge | Shared with provider | Service-based | Strong when a nearby location exists | Moderate | Distributed applications and customer-facing services |
| SD-WAN | Policy-driven | Equipment or subscription dependent | Improves path selection | Moderate to high | Multi-site businesses with varied traffic |
| Carrier PoPs | Provider-controlled | Usually access and service fees | Improves network proximity | Lower for the buyer | Businesses seeking better routing without local compute |
The right choice depends on the bottleneck. If the problem is local processing, on-premises edge may fit. If the problem is inconsistent branch routing, SD-WAN is more relevant. If users are geographically dispersed, cloud edge or PoPs may provide proximity without requiring every site to host equipment.
Where Network Edge Services Show Up in Real Life
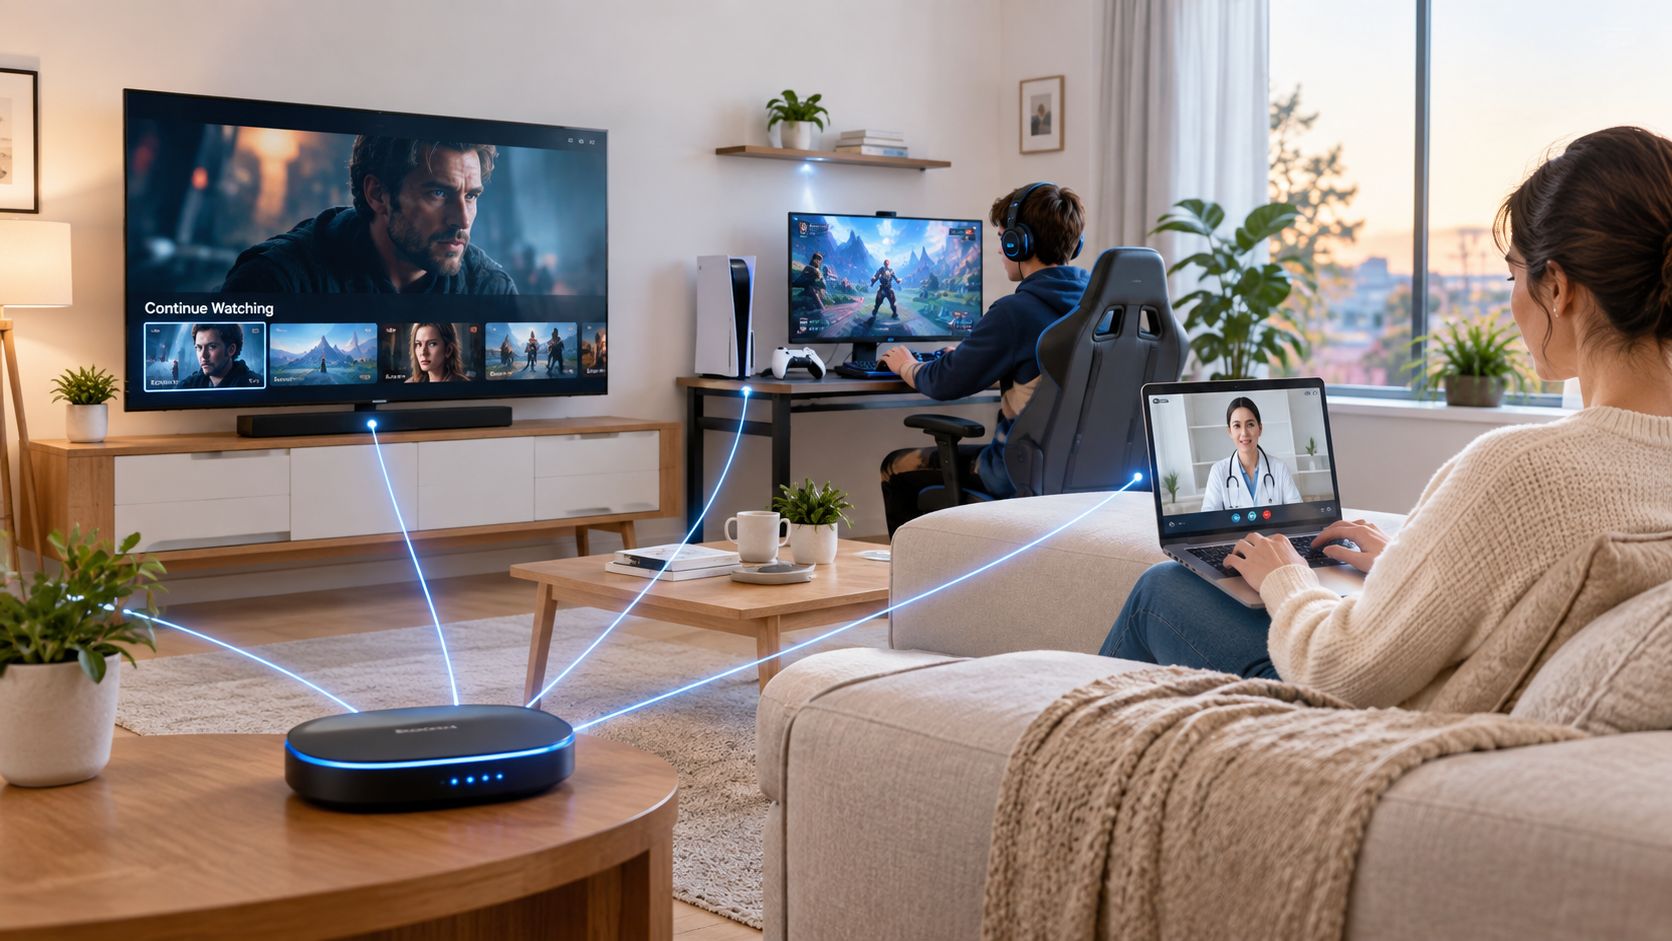
At home, several people can compete for the same connection. One person streams high-resolution video, another plays an online game, and a parent joins a video-heavy telehealth appointment. If every session follows one distant route, the symptoms are familiar: a stuttering game, a frozen call, or a stream that pauses while another device uploads.
Nearby caching and network locations can keep frequently requested content closer to users and give traffic more suitable paths. The edge doesn't create unlimited capacity, and it won't fix a damaged cable or poor wireless coverage, but it can reduce unnecessary travel through the wider network.
A regional retailer faces a similar challenge across its stores. A checkout screen that waits for a distant response can slow a busy queue. A barcode update that reaches the central system late can leave staff working from stale inventory information. Edge routing can keep branch traffic on appropriate paths, while localized processing can handle selected operations closer to each store.
The same principle applies to a logistics company moving warehouse data or a clinic sharing imaging between branches. The central system remains important for records, reporting, and coordination, but not every action needs to wait for a round trip to a remote region.
For a small business, the first step may be better visibility rather than a major architecture change. A retail operator evaluating tools such as ShopSight for connected business operations should ask which transactions need immediate responses, which can tolerate delay, and where a local failure would affect staff or customers.
This short visual provides another way to see how connected devices depend on a coordinated local network:
The Performance and Security Benefits That Matter
Latency is the clearest reason businesses consider an edge design. A large-scale study measured 8,456 end users, 6,341 edge servers, and 69 cloud locations. It found that 58% of users could reach a nearby edge server in under 10 milliseconds, compared with 29% reaching a comparable cloud location, as reported in the latency study published on arXiv. Proximity improves the network journey before application processing begins.
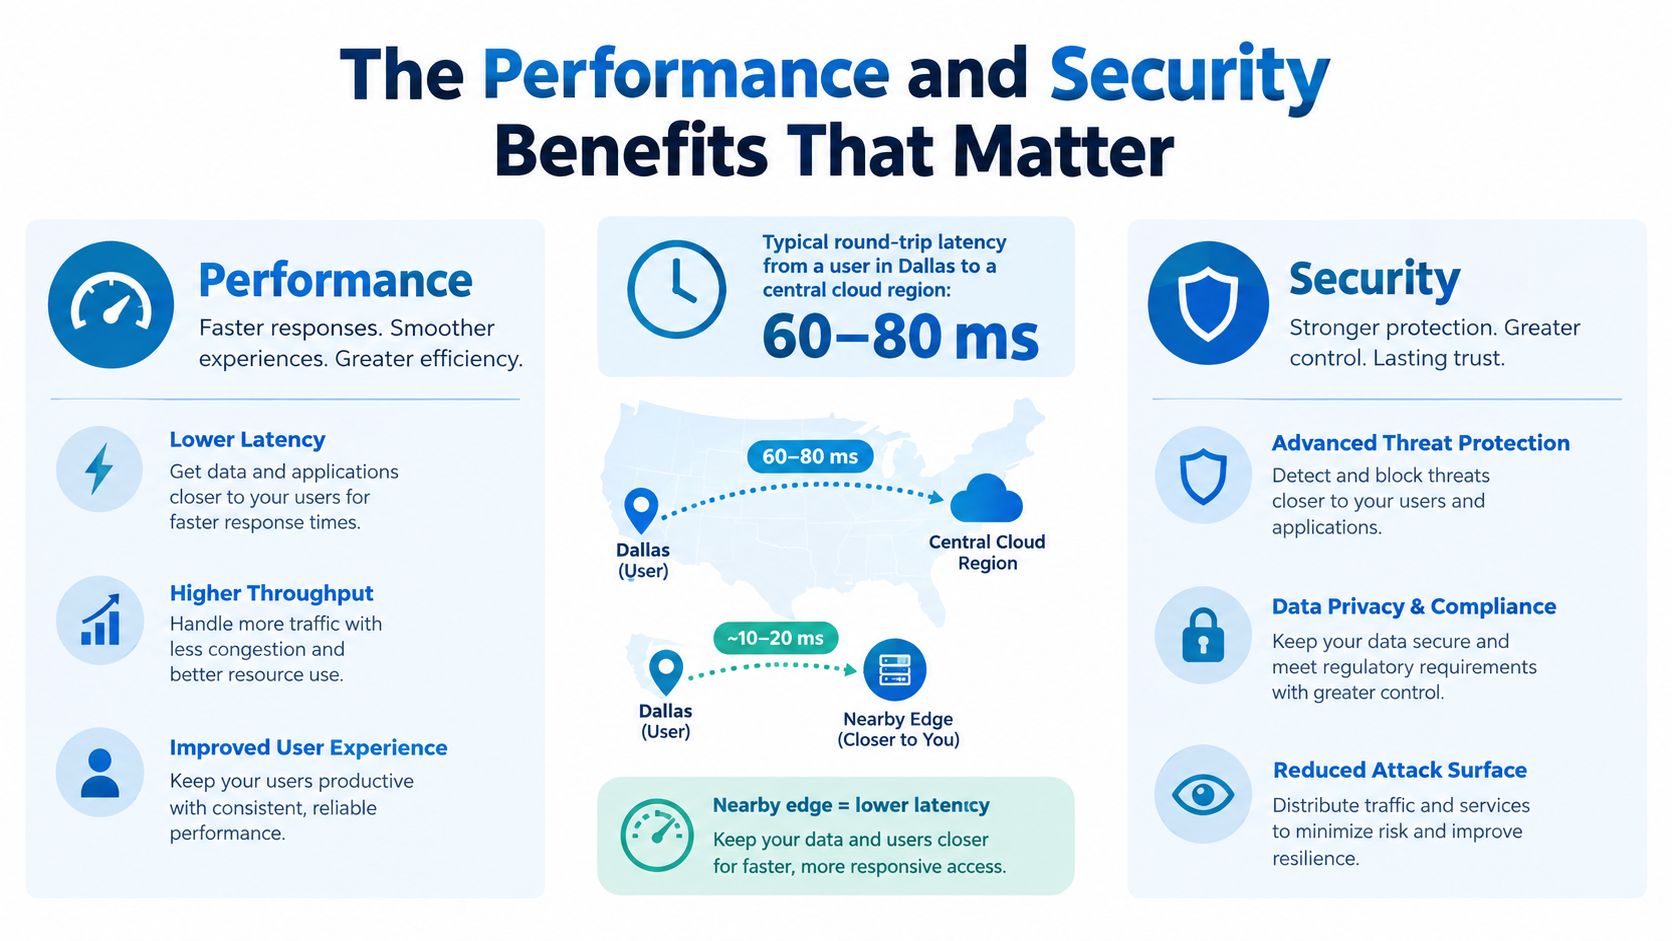
That difference matters most when people notice delay immediately. Voice and video applications need stable delivery, not just high download capacity. Transaction systems need quick acknowledgments. Remote desktops feel unpleasant when keystrokes and screen updates travel through a congested or distant path.
Performance gains have a practical boundary
Edge placement can support:
- Lower round-trip delay: Requests travel to a nearer service location.
- More consistent paths: Traffic steering can select routes based on policy and availability.
- Local processing: Devices can send selected data to nearby compute instead of transferring everything to a central cloud.
- Better content delivery: Frequently requested files or application elements can be cached near users.
These benefits don't mean an edge service automatically improves every application. A workload that already performs well in a central region may gain little, while an application that depends on constant local interaction may gain much more.
Security follows the same geography
An edge location can act as an enforcement point for traffic inspection, access policies, segmentation, and denial-of-service filtering. Placing controls near users and branches helps the organization apply consistent rules before traffic reaches internal systems or sensitive services.
NTT's 2023 Edge Advantage Report found that nearly 70% of enterprises were using edge to address critical business challenges. The report also stated that more than 8 in 10 organizations expected their dependence on third-party edge services to grow over the following two years, while 80% of respondents felt their edge investment was delivering on its promise. Those figures describe adoption sentiment, not a guarantee for an individual buyer.
Choosing Between Managed Edge and the DIY Approach
A managed edge service transfers much of the operating burden to a provider. The provider designs the service, supplies or manages equipment, applies configurations, monitors the environment, and handles updates according to the service agreement. That model suits a business with multiple locations or hybrid workers but without a dedicated network team available to manage every routing and security event.
The do-it-yourself route gives your team direct control. You buy the hardware, configure firewalls and routing, connect different providers, monitor alerts, test failover, and maintain the software. It can make sense for a single site, a technically capable IT department, or an organization that needs unusual customization.
The purchase price isn't the whole comparison. DIY also consumes staff time during incidents, patch windows, migrations, and vendor escalations. A missed firmware update can create security exposure, while a problem involving several suppliers can leave each one arguing that another service owns the fault.
Compare the operating model
| Question | Managed edge | DIY edge |
|---|---|---|
| Who designs the service? | Provider with customer input | Internal team or hired consultants |
| Who monitors it? | Provider's operations team | Internal staff and selected tools |
| Who applies updates? | Provider under agreed procedures | Internal staff |
| How much customization is available? | Within the provider's service model | Broad, if staff can support it |
| Where does accountability sit? | More centralized | Split across internal teams and vendors |
A business owner should ask how the network will be supported at the least convenient time, not only how it will be installed. If your team would rather focus on customers, employees, and core operations than routing tables and firewall policies, a managed model usually deserves serious consideration.
Selection Criteria and ROI for Network Edge Services
Treat edge spending as an investment decision, not a technology upgrade. Start by documenting the pain in business terms: frozen calls, slow transactions, branch outages, support tickets, delayed file transfers, or time spent troubleshooting inconsistent application access.
Then use a vendor-neutral checklist:
- Workload fit: Identify which applications need quick responses and which can remain centralized.
- Location coverage: Check whether the provider has useful PoPs near employees, branches, customers, and cloud destinations.
- Service commitments: Review uptime, latency, response, restoration, and escalation terms in the SLA.
- Integration: Confirm compatibility with your existing WAN, internet connections, cloud providers, voice systems, and security controls.
- Security posture: Ask how the provider handles inspection, segmentation, logging, updates, and incident response.
- Total cost: Include equipment, licenses, installation, cross-connects, egress, professional services, support tiers, and future expansion.
Build the payback from your own records
Count the hours employees lose when an application is unavailable or painfully slow. Record how often support staff investigate branch connectivity, how many calls fail during busy periods, and what an outage delays. If the proposal reduces those costs, compare the estimated operational savings with the complete recurring and one-time price.
Avoid using a vendor's benchmark as your business case. A small organization may gain more from reliable branch routing and simpler support than from local compute. Teams preparing campaigns or coordinating distributed work can also use CampaignPilot for planning and workflow support, while keeping the network decision tied to measured operational needs.
Buying test: If you can't name the workload, location, or recurring business loss that edge addresses, pause before adding another layer of infrastructure.
How Premier Broadband Simplifies the Edge Decision
A bundled service can make the evaluation easier when the business needs connectivity, traffic management, security, and ongoing operations together. Premier Broadband's Managed Network Edge combines those functions through the Cisco Meraki platform, with provider-managed deployment, monitoring, configuration, security, and quality-of-service controls.
That structure maps directly to the selection criteria. The buyer can assess where the service operates, how it connects sites and applications, what monitoring is included, how incidents are escalated, and which charges appear on the monthly agreement. A single accountable provider can also reduce the finger-pointing that occurs when internet access, appliances, security policies, and monitoring come from separate suppliers.
The bundle is most relevant to distributed businesses, hybrid workforces, and organizations replacing older private network designs. It may be less appropriate for a simple single-site environment that has no meaningful latency, availability, or security problem. The right outcome is not maximum distribution. It is a service model that solves a specific operational constraint without making the network harder to run.
A sensible onboarding path starts with discovery. The provider documents sites, users, applications, current connections, security requirements, and failure points. It then proposes the service design, confirms the commercial scope, schedules deployment, tests traffic policies and failover, and hands the live environment into monitoring and support. Businesses ready to examine that scope can request a quote from Premier Broadband and use the checklist above to keep the conversation focused on outcomes.
Premier Broadband offers Managed Network Edge for businesses that need secure connectivity, traffic control, monitoring, and scalable support across distributed locations. Visit Premier Broadband to discuss your current network pain points, compare managed edge options with a centralized design, and identify the next practical step.