A customer is waiting on a video call, but the screen keeps freezing. At the same time, employees are reporting slow Wi-Fi, a VoIP call has dropped, and an unfamiliar device has appeared on the guest network. The owner can see that something is wrong, yet nobody is sure who should change the firewall rule, isolate the device, or verify that the phone system will keep working.
That situation captures the core challenge of network management and security for growing businesses. Management keeps connections available, policies consistent, and traffic moving. Security controls who can connect, what they can reach, and how suspicious activity gets contained. When those responsibilities sit in separate tools and separate hands, a small configuration mistake can affect uptime, customer conversations, and employee productivity.
This guide focuses on the practical gap between seeing a problem and fixing it. You'll learn how the managed network edge works, why centralized policies matter, how to protect voice and fiber networks, and what to ask before choosing a managed services provider.
Why Network Management and Security Now Matter Together
A business network used to be easier to picture. There might have been a router, a few desktop computers, and a basic wireless network. Today, the same small office may depend on fiber internet, cloud applications, managed Wi-Fi, VoIP phones, cameras, printers, guest access, and remote administration.
Each service adds value, but each also adds a path that someone must manage. A faster connection doesn't automatically create a safer connection. A new wireless access point can improve coverage while also creating another device, policy, and administrative interface to maintain.
Management keeps the business moving
Network management covers the operational work behind reliable connectivity. It includes routing traffic, monitoring device health, applying configuration changes, tracking performance, and responding when a link or service fails.
Network security controls access and reduces the chance that unauthorized activity will disrupt the business. Firewalls, segmentation, authentication, secure remote administration, DNS protection, and monitoring all contribute to that outcome.
These functions overlap because a security decision can affect performance. A new inspection rule may add processing work. A poorly designed guest network may expose internal resources. A rushed firmware or routing change may interrupt a phone system even when the original goal was to close a vulnerability.
A secure network isn't useful if the controls prevent employees from working. A fast network isn't dependable if nobody can control who reaches it.
The managed network services market reflects this convergence. One industry estimate places the market at USD 120.74 billion in 2025 and projects it to reach USD 172.04 billion by 2030, with a 7.3% compound annual growth rate. See the managed network services market estimate for the source and scope of those figures.
The business impact is immediate
For a small business, network problems rarely stay inside the IT department. A dropped VoIP call can make a customer repeat sensitive information. Slow cloud access can delay an invoice. An exposed management interface can let an attacker alter policies across a site instead of affecting only one laptop.
The answer isn't just buying more monitoring screens. The business needs a clear operating model that identifies the person or provider who reviews an alert, approves a change, tests the result, and rolls back the change if service quality falls. That is where network management and security become one business responsibility.
Understanding the Managed Network Edge
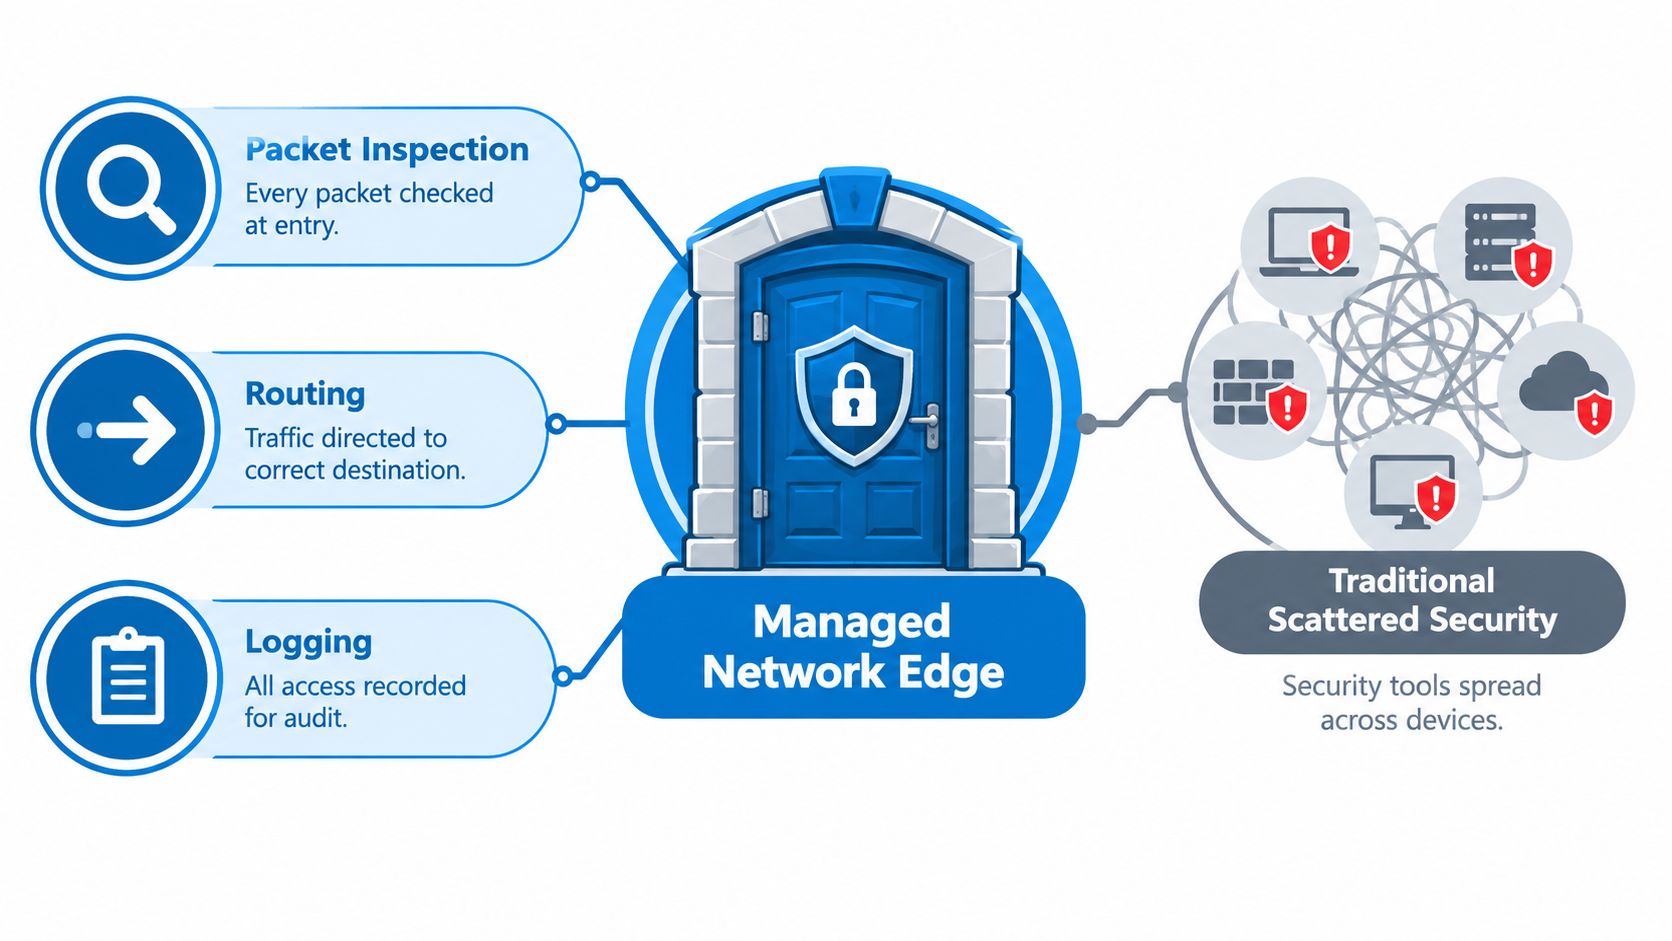
Think of the network edge as the front door of your business. Employees, customers, cloud services, remote workers, phones, and guest devices all pass through it or depend on its decisions. A managed edge places professional oversight at that entrance instead of leaving every switch, access point, firewall, and router to enforce disconnected rules.
Managed network edge: A centrally managed point of connectivity and control where traffic is inspected, routed, governed, and logged before it reaches business resources.
The edge can be a physical appliance, a provider-managed service, or a combination of network and security functions delivered through one operating platform. Its exact location depends on the design, but its role stays consistent. It creates a common place to apply policy and observe what is happening.
Four functions belong at the entrance
Firewalling decides which traffic may enter, leave, or move between network segments. A rule should reflect a business need, such as allowing phones to reach the voice service while preventing guest devices from reaching office file shares.
Routing sends approved traffic to the right destination. It determines whether an application uses the internet connection, a private path, a VPN tunnel, or another internal segment.
Traffic monitoring gives the operator evidence about performance and behavior. Monitoring can reveal an overloaded link, unusual access attempts, repeated authentication failures, or a configuration change that coincided with a service problem.
Policy enforcement turns the business's security decisions into repeatable controls. Instead of asking someone to configure every device manually, a centralized policy can apply the same access, segmentation, and administrative rules across locations.
That consolidation reduces operational sprawl. A better standalone router may improve throughput, but it doesn't by itself establish ownership for monitoring, policy review, incident response, or change approval. A managed edge connects those activities.
Businesses evaluating adjacent digital services can also review Premier Broadband's business solutions while considering how connectivity and network operations fit together. The important question is whether the provider can manage the complete path from deployment through daily support, not whether one box has a longer feature list.
How Network Security Evolved Into Managed Services
Network security didn't begin as one unified discipline. As enterprise networks became more complex in the 1990s and early 2000s, organizations added specialized products to address specific problems. Firewalls controlled unwanted traffic. Virus scanners examined files. Encryption standards protected communications. Each tool had a useful job, but each also created another console, update process, and policy boundary.
Mainstream firewalls and virus scanners arrived around 1995, while SSL and IPsec became standardized around 1998. AES followed in 2001. These milestones helped organizations protect communication and devices, but they also made coordination more important because security decisions now affected more parts of the network.
Point products created a management problem
A business might have one interface for firewall rules, another for intrusion detection, another for antivirus, and separate systems for content filtering and access control. Each product could report a warning without explaining who should act, whether the warning affected another system, or how the change should be tested.
The early 2000s brought unified threat management appliances that combined firewall, IDS/IPS, antivirus, and content filtering in one platform. The history of network security shows why this shift mattered. Centralizing policy enforcement reduced the number of places where an operator had to make or verify a security decision.
That lesson still applies to a small business. Consolidation isn't valuable because fewer product names sound simpler. It's valuable because fewer disconnected control points make it easier to answer practical questions:
- Who changed the rule?
- Which locations received the change?
- Did the change affect voice or guest traffic?
- Was the result checked?
- Can the provider restore the previous configuration?
Integration continues at the edge
Modern managed edge services extend the same idea across fiber connectivity, firewalling, VPN access, segmentation, Wi-Fi, and monitoring. The platform may still contain specialized functions, but the operator sees them through a coordinated operating model.
This history also explains why buying separate products doesn't automatically produce strong network management and security. Integration must include people, policies, and change workflows, not just hardware that happens to share a chassis.
Network Security Best Practices You Can Actually Follow
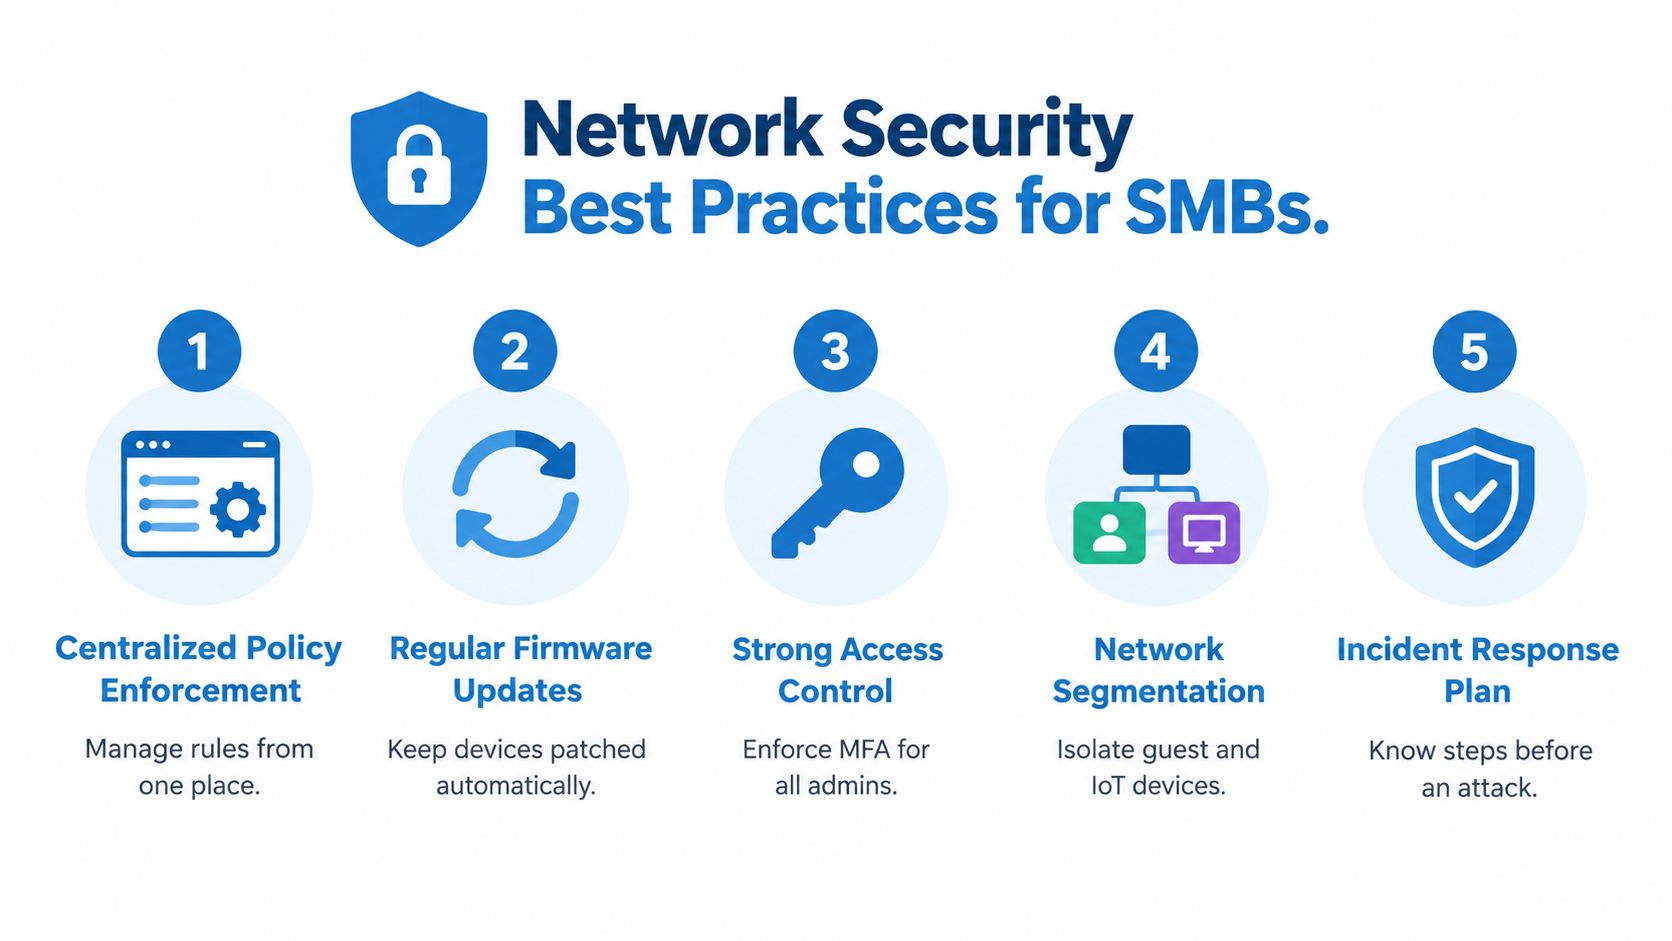
Security advice becomes useful when it changes what someone does next. Microsoft's cloud security benchmark recommends centralized policy enforcement, standardized firewall and routing management, and continuous monitoring with analytics to reduce configuration drift and improve visibility across network assets. The Microsoft network security benchmark provides the technical foundation, but an SMB can turn it into a manageable operating checklist.
Start with one policy source
If an administrator changes a firewall rule on one device but forgets a second device, the business has created policy drift. One location may block a risky connection while another still permits it. Centralized enforcement gives the team one place to review the intended policy and apply it consistently.
Standardized firewall and routing management matters for the same reason. A provider or internal administrator should use repeatable templates, documented approvals, and a clear record of changes rather than making every adjustment from memory.
Separate systems that don't need to trust one another
Segmentation places different types of traffic into separate zones. Guest Wi-Fi, employee devices, voice systems, cameras, and management interfaces shouldn't automatically share the same access path.
A segment limits the damage from a compromised device and makes troubleshooting clearer. If a guest device behaves suspiciously, the operator can restrict the guest zone without interrupting the phone system.
DNS hardening deserves similar attention. DNS helps devices find services, so protective controls can block known malicious destinations and make suspicious lookups easier to investigate. Treat DNS protection as part of the network edge, not as an optional browser feature.
Watch for drift and define the response
Continuous monitoring should identify more than whether a device is online. It should help operators spot unexpected rule changes, altered routes, failed authentication attempts, abnormal traffic, and degraded service quality.
A practical order of operations looks like this:
- Centralize policy: Decide where firewall, routing, and access rules are managed.
- Protect administration: Limit who can reach management interfaces and require strong authentication.
- Segment traffic: Separate guest, voice, IoT, employee, and management networks where appropriate.
- Harden DNS: Add protective filtering and review unusual resolution activity.
- Test response: Confirm who approves, performs, verifies, and reverses a change.
For broader implementation guidance, businesses can review this resource on protect your systems in 2025. The checklist matters most when each item has an owner and a review routine.
The Hidden Gap Between Detecting and Fixing Problems
A monitoring dashboard can turn red while the business remains exposed. The screen may identify a failed login, a suspicious device, or a firewall change, but it doesn't automatically decide whether to block traffic, call a customer, preserve evidence, or roll back a configuration.
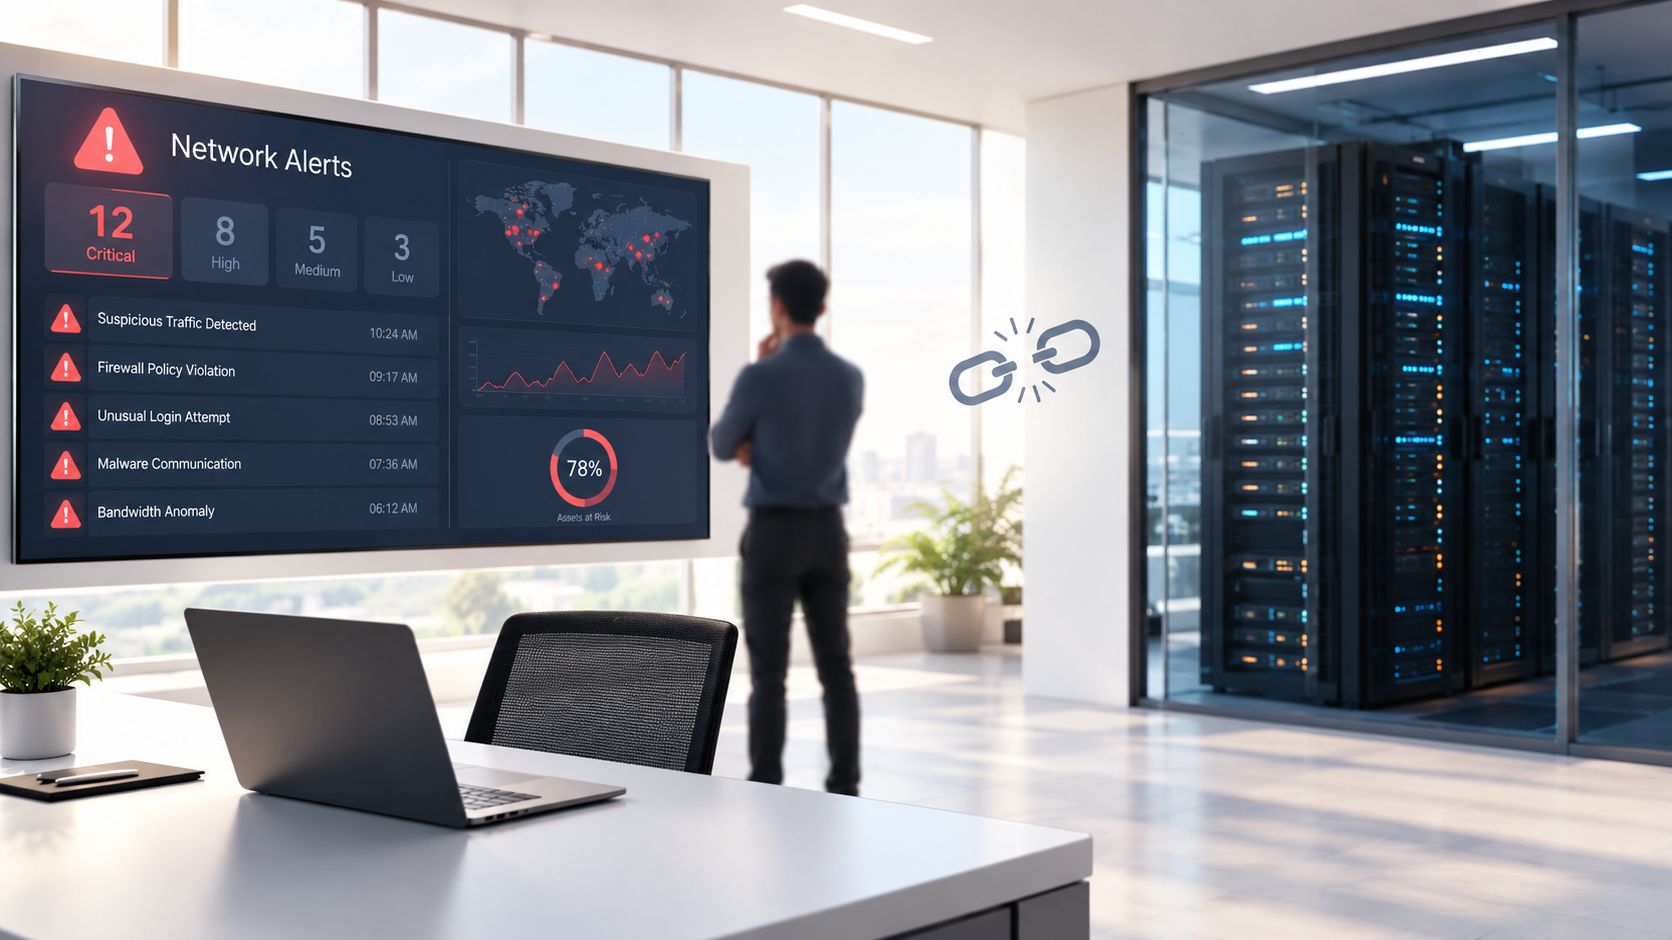
The gap between detection and execution is where many small businesses struggle. An employee notices a problem and sends a message. Someone else has the firewall credentials. A manager must approve the change. The person with access isn't available, or nobody knows how to test whether the fix affected VoIP, Wi-Fi, or cloud applications.
Visibility doesn't equal operational readiness
A 2026 survey found Zero Trust adoption stalled at roughly 55% to 60%, while the share of organizations still in the learning phase rose from 20% to 31%. The survey commentary on the operational security gap suggests that many organizations understand the framework but struggle to put it into daily practice.
That pattern applies beyond Zero Trust. A business may understand least privilege, segmentation, and continuous verification, yet still rely on informal approvals and manual handoffs. The result can be a rule that is too broad, a device that remains connected too long, or a change that fixes one exposure while creating another.
Operational rule: Every important alert should have a named owner, an approved action, a verification step, and a rollback path.
A provider should document those steps before an incident. If a suspicious device appears during a customer call, the operator needs to know whether isolation can happen immediately, who receives the notification, and how the team confirms that legitimate services remain available.
Connect security work to business service
The workflow should include business impact. A firewall change on a conventional office network may interrupt web access. The same change on a converged fiber network may affect phones, video, guest Wi-Fi, and remote workers at once.
Teams that measure web performance or check web traffic for your plumbing company may focus on customer acquisition and site visibility, but service availability also depends on the underlying network workflow. A website, phone line, and cloud application can all suffer when the person making a security change cannot see the broader service dependencies.
The management process should therefore record what changed, why it changed, who approved it, and what users experienced afterward. A centralized platform can help, but the business still needs a human decision process.
For businesses exploring related traffic and collaboration services, Premier Broadband's business connectivity options can be evaluated alongside the provider's approach to ownership, escalation, and change control. The deciding factor isn't the number of alerts. It's whether an alert leads to a safe, accountable action.
Architecture and Deployment Considerations for Converged Networks
A converged network carries several kinds of business traffic across shared infrastructure. Fiber may support internet access, VoIP, video meetings, guest browsing, cameras, and remote administration. That design can be efficient, but the network must distinguish traffic types before congestion or a security event affects every service together.
Voice deserves special treatment because callers notice delay, jitter, and packet loss immediately. NIST recommends IPsec or SSH for remote management and auditing of VoIP systems, while research on VoIP security finds that end-to-end protection can reduce quality of service depending on available bandwidth and the encryption algorithm. The NIST VoIP security guidance supports a balanced design, secure administration paired with low-latency choices and voice segmentation.
Build the traffic boundaries first
A voice VLAN separates phone traffic from guest browsing and many general-purpose devices. Quality-of-service rules can then prioritize voice where appropriate, while firewall policies restrict which systems can communicate with the voice segment.
Management access should sit apart from the data plane. An administrator shouldn't reach a firewall, switch, wireless controller, or voice platform through the same open path used by ordinary users. Restrict administrative access, require strong authentication, and log the activity.
Encryption creates a genuine engineering trade-off. Stronger protection improves confidentiality and integrity, but tunnel processing and encryption overhead can add delay. A provider should test the selected method under realistic load instead of assuming that every secure configuration will produce identical call quality.
Map the need to the design
| Business Need | Architectural Choice | Why It Matters |
|---|---|---|
| Reliable voice quality | Voice VLAN, QoS, and low-latency encryption | Keeps calls separate from competing traffic and limits avoidable delay |
| Safe guest access | Isolated guest segment with restricted internal reach | Prevents visitors from reaching business systems |
| Protected remote management | IPsec or SSH, restricted administrative paths, and logging | Secures administration while creating an audit trail |
| Multi-service fiber access | Centralized edge policies and traffic visibility | Gives operators one place to review interactions between services |
| Fast incident response | Defined approval and rollback workflow | Converts an alert into a controlled operational action |
Before deployment day, ask the provider to identify each traffic class, document the intended segmentation, test a busy voice period, and show how an emergency policy change is approved. Businesses can also review Premier Broadband's Vista WA chat button service when assessing customer communication requirements alongside network design. The broader principle is simple: protect the control path without starving the services that keep the business operating.
How Premier Broadband Simplifies Network Management and Security
A business can assemble fiber internet, a firewall, wireless access points, VoIP, monitoring software, and separate support contracts. That approach gives the owner control over each purchase, but it can also create unclear responsibility. When a call drops after a firewall change, one vendor may blame the network while another points to the voice platform.
Premier Broadband offers a Managed Network Edge that combines connectivity, firewall controls, segmentation, and monitoring within one operating model. Its business portfolio also includes 100% fiber business internet with symmetrical upload and download speeds, no-contract unlimited-data plans, managed Wi-Fi, and VoIP services. Those are product characteristics described by the publisher, not a guarantee that every deployment will produce the same result.
Compare operating models, not just equipment
With a DIY arrangement, the owner or internal IT contact may need to coordinate several tasks:
- Connectivity: Confirm the fiber link, routing, and service performance.
- Security: Maintain firewall policies, access controls, updates, and alerts.
- Voice: Protect call quality while changing shared network settings.
- Wi-Fi: Manage employee, guest, and device access across the premises.
- Response: Decide who acts when monitoring identifies a problem.
A managed approach can assign more of those responsibilities to one provider. That doesn't remove the need for business decisions. The owner still needs to define acceptable access, approve important changes, and understand escalation terms. It does make the path from detection to action clearer.
Protect the management plane
Security should cover the interfaces that control the network, not only the endpoints that use it. A provider-managed model should explain how administrative access is authenticated, where management traffic is allowed, how changes are logged, and how the team responds if a controller or orchestration layer is threatened.
Premier Broadband's shipping rules service is separate from network security, but it illustrates a useful evaluation habit. Look at the complete service relationship and the actual operating responsibilities, rather than judging a provider by one feature in isolation.
The practical value of consolidation is accountability. One partner can coordinate connectivity, voice, Wi-Fi, edge security, and the related change workflow. Before signing, ask for the service boundaries in writing so everyone knows which actions happen automatically, which require approval, and which remain the customer's responsibility.
Your Next Steps Toward a Safer, Simpler Network
Start with a short review this week. You don't need a large audit to identify whether your business has a management-plane problem. You need clear answers to a few operational questions.
Run a small-business self-assessment
Who can change the firewall? Write down the people and providers with administrative access. If nobody can identify the current owner, the business already has a change-control weakness.
How is voice traffic separated? Confirm whether phones use a dedicated VLAN or another documented control. Ask what happens to call quality when guest traffic or a large file transfer consumes capacity.
What happens after an alert? Follow one recent alert from detection to resolution. Identify who reviewed it, who approved the action, who made the change, and how the team verified the result.
Which interfaces are exposed? Inventory the administrative paths for firewalls, switches, access points, controllers, and VoIP systems. Restrict access that doesn't need to be public or broadly reachable.
Ask providers questions that reveal ownership
A useful provider conversation should cover more than bandwidth and hardware. Ask:
- How are firewall, routing, DNS, and segmentation policies managed across locations?
- Which changes happen automatically, and which require customer approval?
- Who responds to a high-priority alert outside normal business hours?
- How does the provider isolate management access from ordinary user traffic?
- How are administrator identities protected and logged?
- What tests confirm that a security change hasn't damaged VoIP quality?
- What is the rollback process if a change causes an outage?
- Which services are monitored together, and where does the provider's responsibility end?
Management platforms deserve this scrutiny because attackers increasingly target the systems that control networks. Independent reporting tracked 158 security advisories across 17 vendors, involving 1,699 vulnerabilities, including 71 remotely exploitable without authentication and critical flaws in firewall management and identity systems. The report on network management system attacks shows why protecting controllers and orchestration layers belongs in an SMB security plan.
A safer network doesn't require a small business to become a security vendor. It requires clear ownership, centralized control, sensible segmentation, and a response process that turns detection into action. Consolidating those responsibilities with a capable partner can make network management and security practical even without a dedicated IT department.
Premier Broadband provides business fiber internet, VoIP, managed Wi-Fi, and Managed Network Edge services that bring connectivity, security controls, monitoring, and operational support into one provider relationship. Visit Premier Broadband to review the available business solutions and discuss a network design that protects management access while preserving uptime and voice quality.